How your access is protected
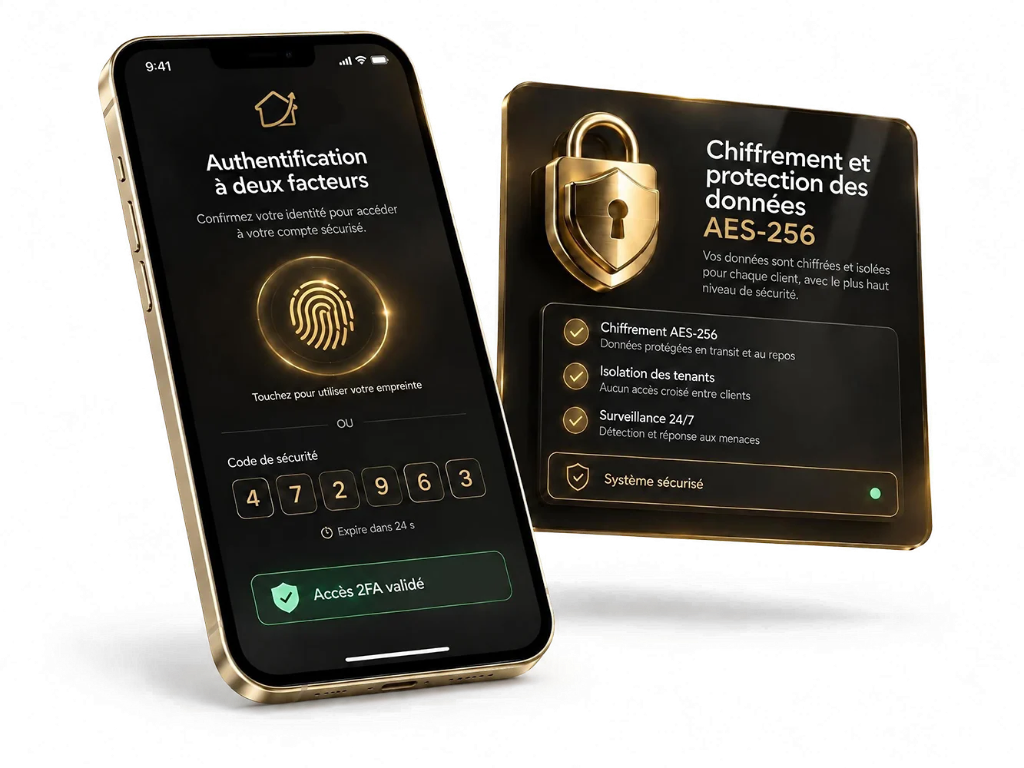
You sign in
Password or sign-in via an external account: a classic first step, but never enough on its own.
You validate a second factor
Code received by email, or an authenticator app (compatible with Google Authenticator). Without this step, the session stays incomplete.
Even after social sign-in
OAuth does not bypass the rule: no complete session without 2FA. Your cockpit does not open “just because Google said yes.”
You work in a secure session
Once 2FA is validated, you access the cockpit. Access remains tracked on the platform side, without exposing your codes.
Your data, isolated and protected
Each property has its secrets encrypted separately. Card numbers never pass through Room Copilot: Stripe handles them.
Strong encryption at rest
Sensitive information (channel access, authentication secrets) is encrypted. The clear key is never stored in the database.
Isolation between properties
No cross-access between customers: your house data stays separate from other hosts’.
Card payments with Stripe
Card number, security code: never stored with us. Guest collections go through Stripe.
What this means for you
Operational peace of mind: protected account, siloed data, honest marketing claims.
Your cockpit does not open halfway
Without a second factor, no complete session. Even if a password leaks, access stays blocked without the code.
2FA of your choice: email or app
One-time email code, or authenticator on the phone: you choose the mode that suits you.
Property secrets protected
Channel connections and sensitive secrets are encrypted and isolated: it is not a shared vault across all customers.
Neighbors do not see your data
Multi-property architecture: strict isolation, no cross-access between accounts.
No card data with us
Card number, CVC, and PIN stay with Stripe. Room Copilot does not store what you do not want leaked.
Biometrics = your device, not us
Touch ID or Face ID secure access to your phone or password manager. That is not biometrics registered by the platform.